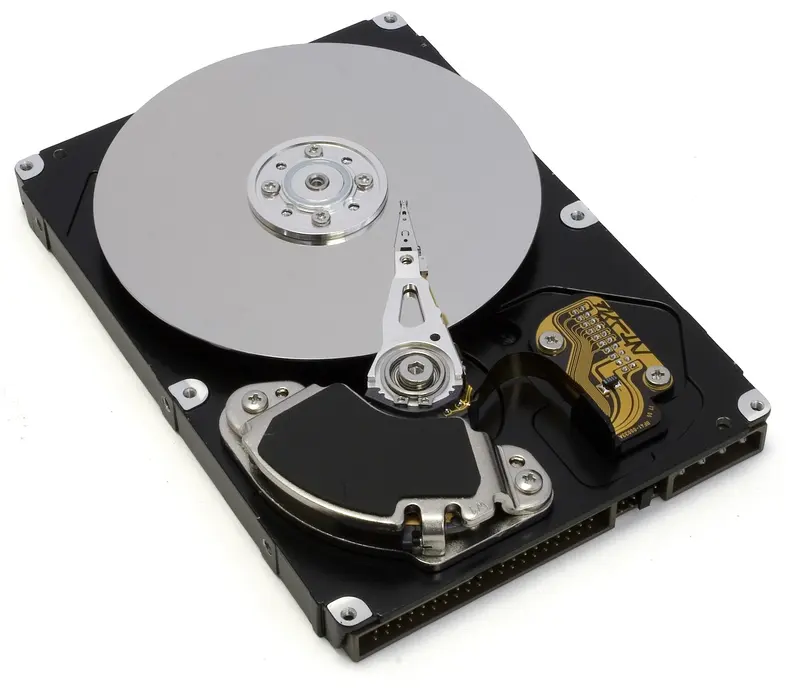
The security principle covers disposal
UK GDPR requires personal data to be kept secure using appropriate technical or organisational measures — the security principle, in Article 5(1)(f) and Article 32. It covers the whole life of the data, including when the equipment holding it is disposed of. The ICO’s guidance says that whoever is responsible for security needs to know about commissioning and disposing of IT equipment.
For small organisations the ICO’s advice is simple: make sure no personal data is left on computers, laptops, phones or other devices before they are disposed of, using deletion software or a specialist wiping service.
What the ICO expects to see
The ICO’s audit framework expects organisations to:
- keep records proving secure disposal — destruction logs, and certificates from the third parties who do it
- wipe, degauss or securely destroy hardware that holds personal data
- document the procedure, with management sign-off
- keep equipment awaiting disposal in a locked area
- carry out due diligence or audits on disposal contractors.
Your ITAD company is your processor
If an ITAD company wipes or destroys your data, it is acting as your processor. UK GDPR (Article 28) requires a written contract that obliges it to:
- act only on your documented instructions
- keep its staff bound by confidentiality
- apply appropriate security (Article 32)
- use sub-processors only with your authorisation, on equivalent terms
- let you audit it.
Approved certification schemes can help a processor show that it offers “sufficient guarantees”.
ADISA: an ICO-approved scheme
The ICO has approved ADISA ICT Asset Recovery Certification 8.0 as a UK GDPR certification scheme. It was first approved in July 2021, and updated criteria reflecting the Data (Use and Access) Act 2025 were approved in March 2026. Certification is issued by ADISA Certification Ltd, which is UKAS accredited.
You can check a company on the ADISA Certification register, which also lists lapsed and withdrawn certifications. On Green ITAD, ADISA certification shows as verified only once we have found it on that register.
Some ICO guidance is being reviewed following the Data (Use and Access) Act 2025, which became law on 19 June 2025. Check the ICO’s website for the latest version.
How the data is destroyed
For the methods — software erasure, cryptographic erase, shredding and degaussing — and the standards behind them, see data wiping and destruction standards. For questions to ask a provider, see the checklist. Find companies offering data destruction.
Sources
- ICO: A guide to data security
- ICO: Practical ways to keep your IT systems safe and secure
- ICO data protection audit framework: asset management
- ICO: What needs to be included in the contract?
- ICO certification scheme register: ADISA ICT Asset Recovery Certification 8.0
- ICO: Deleting your data from computers, laptops and other devices
This guide is general information, not legal advice. Rules differ between England, Wales, Scotland and Northern Ireland — check with the regulator or an adviser for your situation.